Authenticate with Private Key JWT using Amazon Bedrock AgentCore Identity
AWS Machine Learning published a guide detailing how Private Key JWT client authentication operates within Amazon Bedrock AgentCore Identity. The resource outlines supported grant flows alongside the steps necessary to configure client credentials and logging. It highlights key setup tasks, including signing key creation, public key registration, console configuration, and audit log reviews.
Key Takeaways
- AWS Machine Learning released an instructional walkthrough detailing how Private Key JWT client authentication functions inside Amazon Bedrock AgentCore Identity.
The guide explains the mechanics of client authentication and reviews the specific grant flows supported by the system.
- To implement this configuration, users generate an AWS KMS signing key and register its corresponding public key with their designated identity provider.
After setting up the signing key, users must configure a credential provider through the AWS Management Console.
- The process concludes with an examination of sample AWS CloudTrail events, which offer clear visibility into agent access logs.
For developers building autonomous workflows, secure authentication mechanisms ensure that AI agents interact safely with external identity systems while maintaining strict access controls and auditability.
- Amazon Bedrock AgentCore Identity supports Private Key JWT client authentication across various grant flows.
Setting up this security model requires generating an AWS KMS signing key and registering its public key with an identity provider.
- AWS CloudTrail events can be reviewed to monitor and audit access requests made by deployed agents.
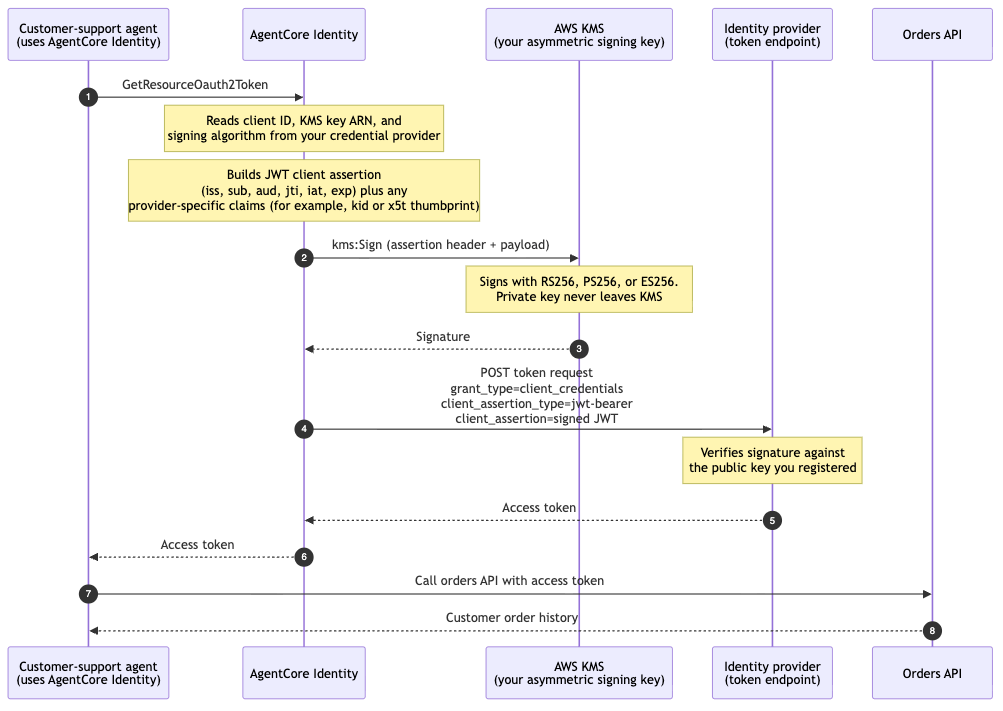
AWS Machine Learning released an instructional walkthrough detailing how Private Key JWT client authentication functions inside Amazon Bedrock AgentCore Identity. The guide explains the mechanics of client authentication and reviews the specific grant flows supported by the system. To implement this configuration, users generate an AWS KMS signing key and register its corresponding public key with their designated identity provider.
After setting up the signing key, users must configure a credential provider through the AWS Management Console. The process concludes with an examination of sample AWS CloudTrail events, which offer clear visibility into agent access logs. For developers building autonomous workflows, secure authentication mechanisms ensure that AI agents interact safely with external identity systems while maintaining strict access controls and auditability.
Amazon Bedrock AgentCore Identity supports Private Key JWT client authentication across various grant flows. Setting up this security model requires generating an AWS KMS signing key and registering its public key with an identity provider. Administrators configure credential providers via the AWS Management Console to establish authenticated access for AI agents.
For more details please read the original article at AWS Machine Learning.
Continue Learning
Comments
Comments appear only after moderation. Your email identifies your submission to the moderator and is never displayed here.
No approved comments yet.